Managed IT services for insurance agencies have one clock that matters more than any other: the renewal date on a client’s policy. Everything an agency does with technology, from pulling the expiring list to binding the policy, sits on a chain of logins and files, and a break in the chain costs you a client, not just an afternoon.
The renewal is your IT calendar
Agencies don’t have a single busy season. They have renewals every week, and each one runs through the same five stages.
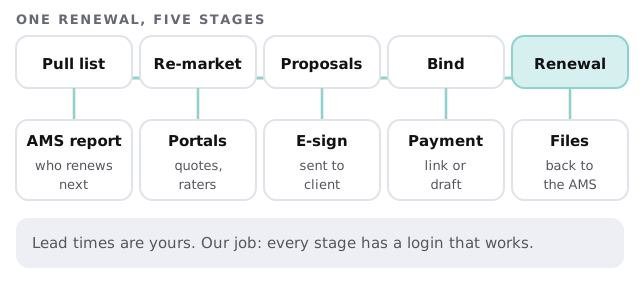
- Pull the list. The agency management system produces who renews next. If it’s slow or down, nothing else starts.
- Re-market. Producers and account managers sign in to several carrier portals and a comparative rater, often within one hour.
- Send proposals. Email, e-signature and shared folders carry the quote to the client.
- Bind. Payment links and carrier confirmations come back through email and portals.
- File it. Declarations and binders are saved into the client’s record, not onto someone’s desktop.
Logins are the real risk
An agency with eight staff and a dozen carriers can end up with a portal account for every pairing of person and carrier. That’s where problems start. Passwords get shared to save time. A producer leaves and nobody knows which portals they had.
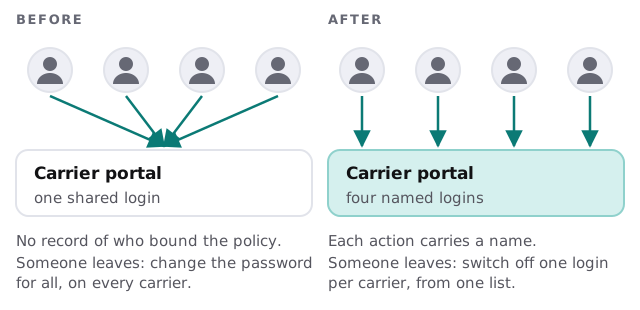
- Use a password manager so each person holds their own credentials.
- Turn on multi-factor sign-in on email first, because email resets every other password.
- Keep a list of which portals each person uses, reviewed when anyone joins or leaves.
- Encrypt laptops and keep phones manageable, because producers work from cars, clients’ offices and kitchens.
A Friday with the system down
It’s 3:40 on a Friday and the agency management system won’t open. Two renewals expire at midnight and one client is waiting on a certificate. In an agency with a plan, someone knows whether it’s the internet connection, the vendor or a laptop. Carrier portals still work from the browser, a recent copy of the renewal list exists outside the system, and the vendor’s support line is already in the notes.
In an agency without one, three people reboot three computers and call the nephew who “does the computers.”
What the data security law asks
The NAIC’s Insurance Data Security Model Law is a model, and states adopt their own versions, so check yours. In the model, Section 4 asks each licensee to keep a comprehensive written information security program based on a risk assessment, sized to the licensee’s business. It covers the licensee’s use of third-party service providers too, which includes your management system vendor and your IT provider. Licensees with fewer than ten employees, counting independent contractors, are exempt from that section. Section 6 sets a 72-hour clock for telling the commissioner about a cybersecurity event.
Read your state’s version before you decide anything. We explain what rules like this ask for. We don’t certify an agency, and the program remains yours.
What to ask a provider
- Have you supported an agency management system, and can you work with its vendor?
- How do you handle carrier portals that insist on a shared login?
- What does a producer’s last day look like on your checklist?
- Which of your own staff can reach our systems?
We’ll answer those on the free IT check, then send a plan and a fixed quote.